Security
Continuous posture scanning and vulnerability management across every estate.
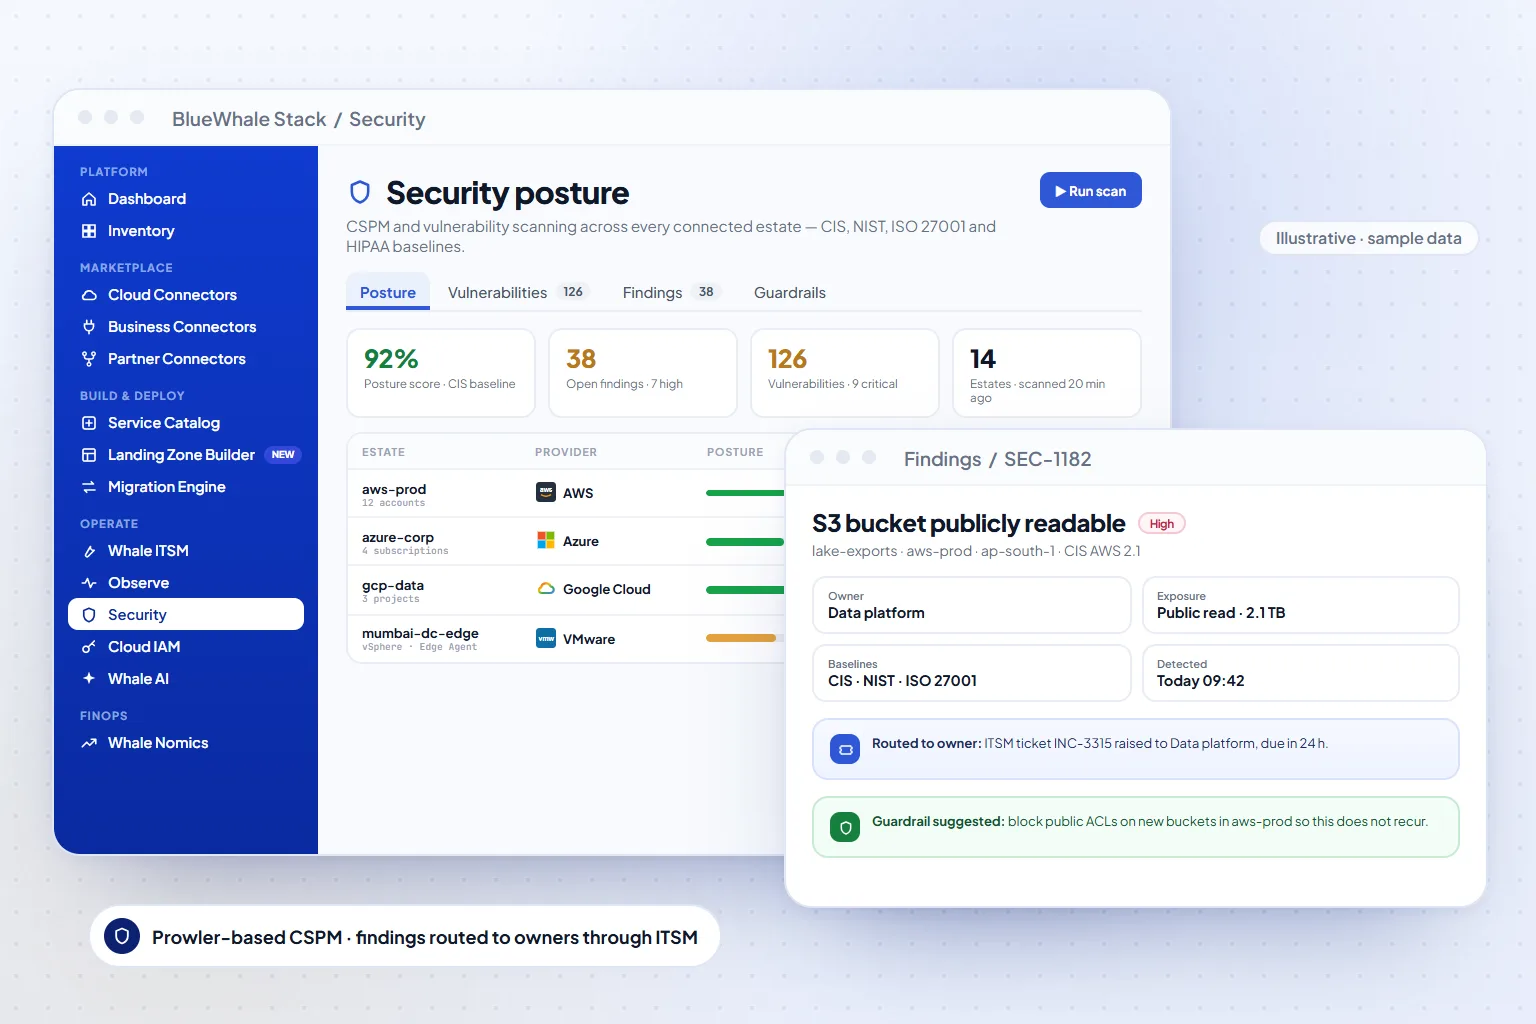
Security gives every connected estate the same posture. Cloud security posture management (CSPM, powered by Prowler) and vulnerability management scan clouds and private estates continuously, check them against CIS, NIST, ISO 27001 and HIPAA baselines, and route each finding to its owner through ITSM.
- Continuous
- Posture and vulnerability scanning, not quarterly reviews
- 4 baselines
- CIS · NIST · ISO 27001 · HIPAA
- Every estate
- Public cloud, private cloud and edge, one posture
Capabilities
What Security does
Posture scanning (CSPM)
Prowler-based checks run across every connected cloud account, surfacing misconfigurations in identity, network, storage and logging.
Vulnerability management
Vulnerabilities are collected per workload and ranked by severity and exposure, so teams fix what matters first.
Baselines and policy
Findings map to CIS, NIST, ISO 27001 and HIPAA controls, with policy-as-code guardrails to stop the same issue recurring.
Owner routing
Each finding is raised to the resource owner as an ITSM ticket and tracked to closure.
How it works
3 steps, from first connection to steady state
Connect
Estates joined through Cloud Connectors are scanned automatically — no extra agents in the cloud.
Scan and score
Posture and vulnerability checks run continuously and roll up into a compliance score per estate.
Remediate
Findings route to owners through ITSM; guardrails prevent recurrence.
Where it fits
One module of one platform
Shared platform
Capabilities
- CSPM scanning across every connected estate (Prowler)
- Vulnerability management with owner routing
- CIS · NIST · ISO 27001 · HIPAA baselines
- Findings raised as ITSM tickets
Also in Security & Identity
Questions
Questions teams ask before turning it on
Scope, permissions and maturity — answered the way we answer them in an evaluation.
01Do we need to install agents in our cloud accounts?
No. Cloud posture checks run through the read-only access Cloud Connectors already hold; private estates are covered through the Edge Agent.
02Which baselines are covered?
CIS, NIST, ISO 27001 and HIPAA today; findings are mapped to the matching control in each.
03How does this relate to Cloud Audit & Evidence?
Security finds and fixes issues; Cloud Audit & Evidence turns the continuously monitored controls into the reports auditors and regulators ask for.
See it on your data
Security, on your own estate — in one working session.
Bring one cloud account or one on-prem site. We connect it read-only during the call, walk the module on your real resources, and leave you with the export.