Security & Compliance
Federated identity, role-based access and a full audit trail across every connected cloud — with data residency and air-gapped options for the most regulated estates.
- 0
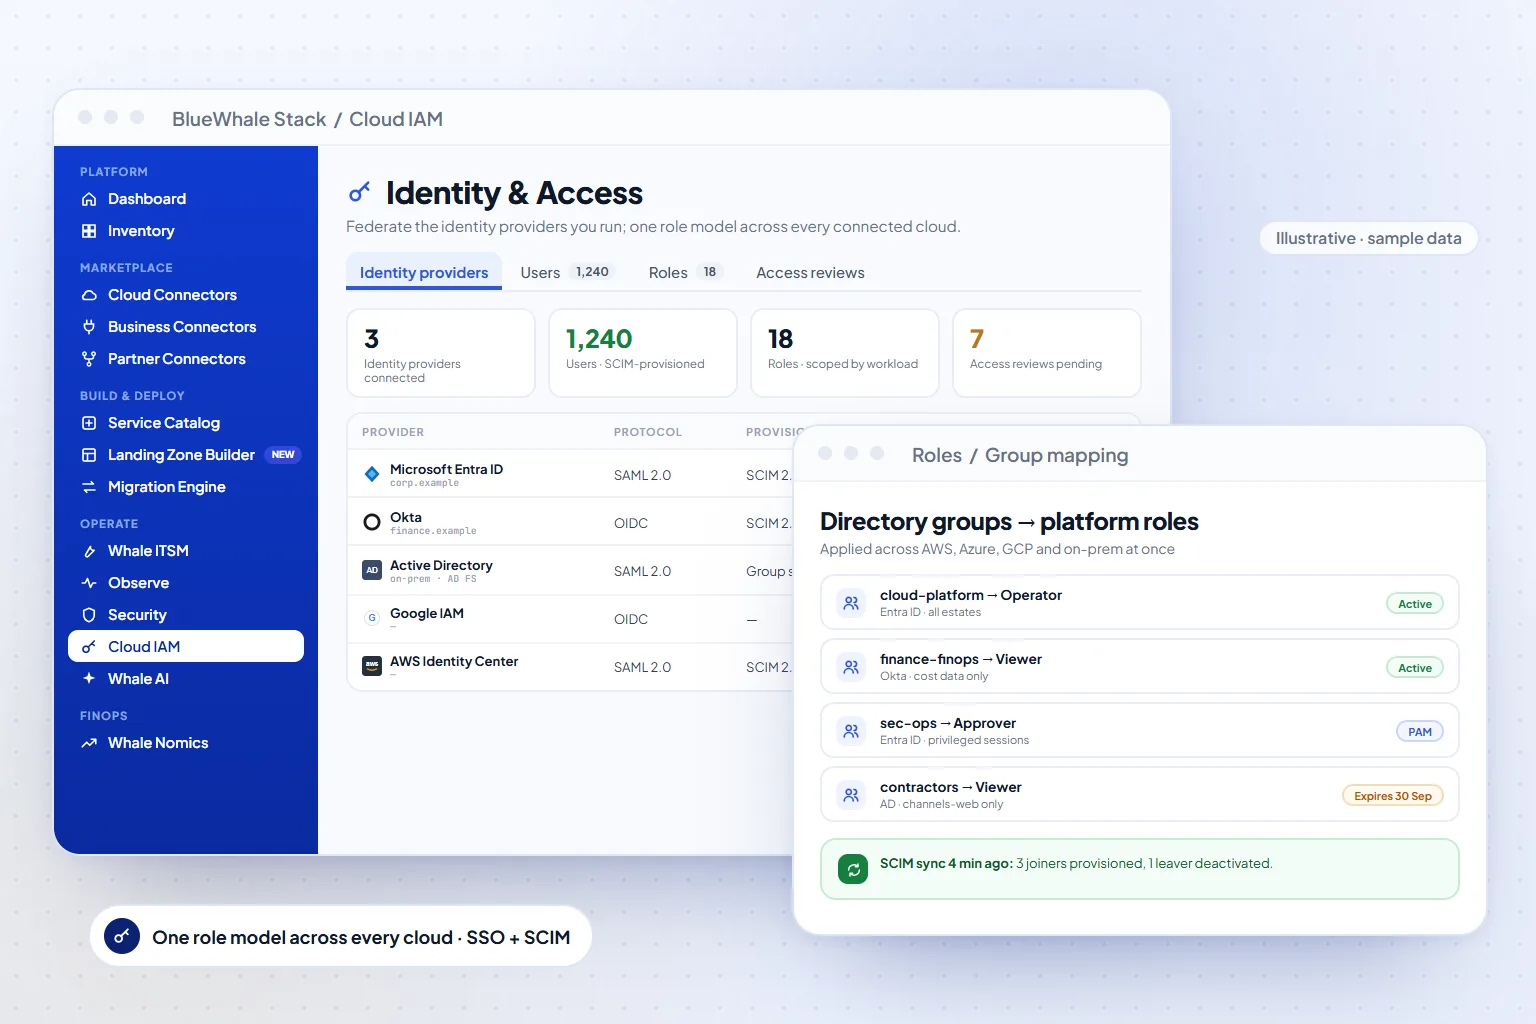
- Identity providers federated — Entra, Okta, Auth0, AWS Identity Center, AD and more
- 5 ISO
- 27001 · 27017 · 27018 · 27701 · 22301, independently audited
- 72 h
- Breach notification commitment; sub-processor changes on 30-day notice
The challenge
Access and audit are fragmented across clouds and tools, and regulators increasingly demand provable residency and a single, trustworthy record of who did what.
- 01
Each cloud has its own IAM, so joiner and leaver hygiene depends on people remembering.
- 02
Audit evidence is screenshots gathered in the two weeks before the inspection.
- 03
Residency is asserted in a policy document and cannot be shown per resource.
How it works
The data path, end to end
- Step 1:
Federate your IdP over SAML 2.0 or OIDC; SCIM maps directory groups to platform roles.
- Step 2:
Role-based access is enforced consistently across every connected cloud and on-prem estate.
- Step 3:
Every action is written to an append-only audit trail.
- Step 4:
Residency pins workloads and records to an in-country region — Mumbai for DPDP, Frankfurt for GDPR.
- Step 5:
Cloud Audit & Evidence monitors controls continuously and produces the report per regime on demand.
Who it's for
CISOs, Heads of Cloud Security and compliance officers in regulated industries.
Recommended editions
Related solutions
Questions
Questions teams ask in the evaluation
Scope, permissions, integrations and what is live today.
01Which certifications does the platform itself hold?
ISO/IEC 27001:2022, 27017, 27018, 27701 and ISO 22301, independently audited; plus a CSA STAR Level 1 self-assessment, a GDPR compliance assessment and a SOC 2 Type II readiness assessment. Signed certificates are in the Trust Center.
02Is MFA enforced?
MFA follows your IdP policy for SSO. In the Government Edition MFA is mandatory on every role and privileged access always runs through PAM with session recording.
03How does residency work on SaaS?
You choose Singapore, Mumbai, Dubai, Frankfurt or Los Angeles and data stays there. For regimes without a SaaS region, BYOC, on-prem or air-gapped deployment keeps everything in-country.
Next step
Security & Compliance, on your own estate.
Bring one cloud account or one on-prem site. We connect it read-only during the session, walk this workflow on your real resources, and leave you with the export.