Six clouds and the datacenter floor, governed as one estate.
One control plane for every estate: a unified inventory across six public clouds and on-prem, governed provisioning, bundled observability and continuous control evidence — SaaS, BYOC or sovereign.
Built for
- Large Enterprises
- IT Teams
- Platform Engineering
- Financial Services
- Retail
- 0
- Modules in the Enterprise Edition
- 6 + on-prem
- Public clouds plus VMware, Hyper-V, Nutanix, OpenShift, KVM
- 50+
- Whale AI use cases grounded in your data
- 0
- Deployment models for this edition — SaaS · BYOC · Sovereign
Regulatory reality
The regimes, and the control that answers each
GDPR / DPDP
What it demands
Personal data kept in-region, processing evidenced
The control that answers it
Region selection per estate — Frankfurt or Mumbai on SaaS, in-country on BYOC; residency enforced and logged
Internal control frameworks (SOC 2-style, ISO 27001)
What it demands
Controls operating continuously with evidence, not sampled quarterly
The control that answers it
Cloud Audit & Evidence: policy as configuration, controls monitored continuously, findings routed to owners
Board and internal-audit reporting
What it demands
One trusted picture of estate, cost and risk
The control that answers it
Reports generated from the same inventory, billing and audit trail the operators use
Vendor security review
What it demands
The platform itself independently assessed
The control that answers it
ISO/IEC 27001, 27017, 27018, 27701 and ISO 22301 certified; SOC 2 Type II readiness assessment complete
Use cases
Four workflows, mapped to the modules that run them
- 01
Identity sync & auto-provisioning from your IdP
Federate Okta, Auth0 or Entra ID; SCIM maps directory groups to platform roles, so a new hire logs in once and is granted the right role — and is offboarded on the next directory sync.
- 02
One inventory across every cloud and on-prem
Discover every resource across six public clouds plus on-prem and hybrid, grouped by workload, with exportable reports for stakeholders and the API for your CMDB.
- 03
Standardized, governed provisioning
Standardise delivery through a governed catalog (AWS live) with approval workflows and Whale AI sizing, integrated with ITSM so every change is tracked.
- 04
Bundled observability & migration assessment
Logs, metrics, traces and SLOs bundled in, and a 6R assessment of on-prem workloads when you are ready to move.
Reference architecture
One governed layer across the whole enterprise estate — nothing re-hosted to adopt it
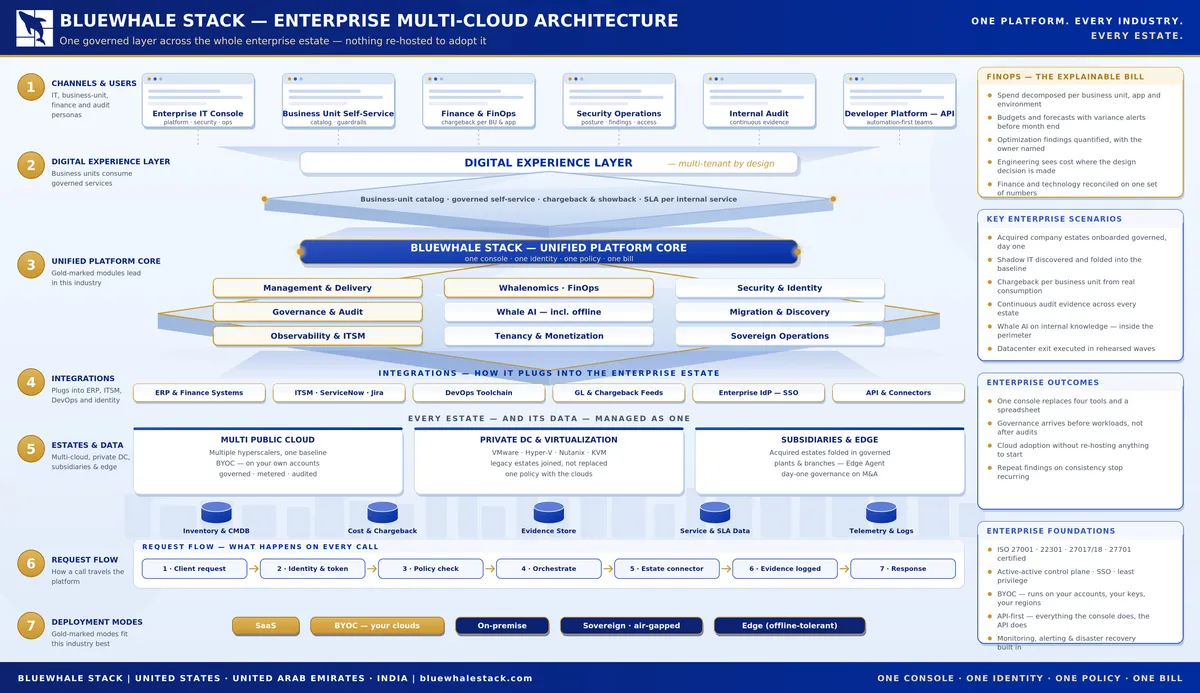 The seven-layer Regulated Enterprise architecture sheetEnterprise Multi-Cloud architecture — open it here, or full screen to read every label
Fig · Regulated Enterprise — reference architecture
5400 × 3120
Enterprise Multi-Cloud architecture
One governed layer across the whole enterprise estate — nothing re-hosted to adopt it
How to read it
- 1Channels & users — The consoles and portals each persona works in
- 2Digital Experience Layer — Catalog, self-service, metering and SLA per service — multi-tenant by design
- 3Unified Platform Core — Nine modules under one console, one identity, one policy and one bill
- 4Integrations — How the platform plugs into the systems the estate already runs
- 5Estates & data — Every estate managed as one, and the data stores that hold the evidence
- 6Request flow — The seven steps every call takes — identity, policy, orchestration, evidence
- 7Deployment modes — SaaS, BYOC, on-premise, sovereign air-gapped and edge — the same build
Gold-marked for Regulated Enterprise
Modules that lead
Deployment modes that fit
Plugs into
ERP & finance systems · ITSM · ServiceNow · Jira · DevOps toolchain · GL & chargeback feeds · Enterprise IdP — SSO · API & connectors
Questions
Procurement, hosting and integration questions
01We already run a CMP and a monitoring tool. What changes?
Both are covered by the platform licence — inventory, catalog and Observe — so the usual outcome is retiring two contracts and two identity systems. Existing tools can stay connected during the transition.
02SaaS, BYOC or sovereign — how do we choose?
SaaS in Singapore, Mumbai, Dubai, Frankfurt or Los Angeles is the fastest start. BYOC runs the control plane in your own AWS, Azure or GCP accounts. Sovereign is for estates that must have no external dependency. All three run the same build.
03How long until we see our whole estate?
A cloud account is inventoried within about 15 minutes of its connector going green; an on-prem site follows the Edge Agent install. Most enterprises have the full picture inside the first week of the 90-day prototype.
Next step
Bring your Regulated Enterprise estate to a working session.
We connect one of your accounts read-only during the session, walk the Regulated Enterprise workflows above on your real resources, and leave you with the control mapping for your regimes.